Immutability has been the greatest improvement on the linux desktop in a long time. I'd never recommend a traditional distro to someone who can't fix or install linux themselves because mutable distros tend to grow warts over time, and diverge from a clean state. Eventually requiring a reinstall to fix.
But immutable distros stay in a clean state, updates become trivial and safe, and can roll back in case of a failure.
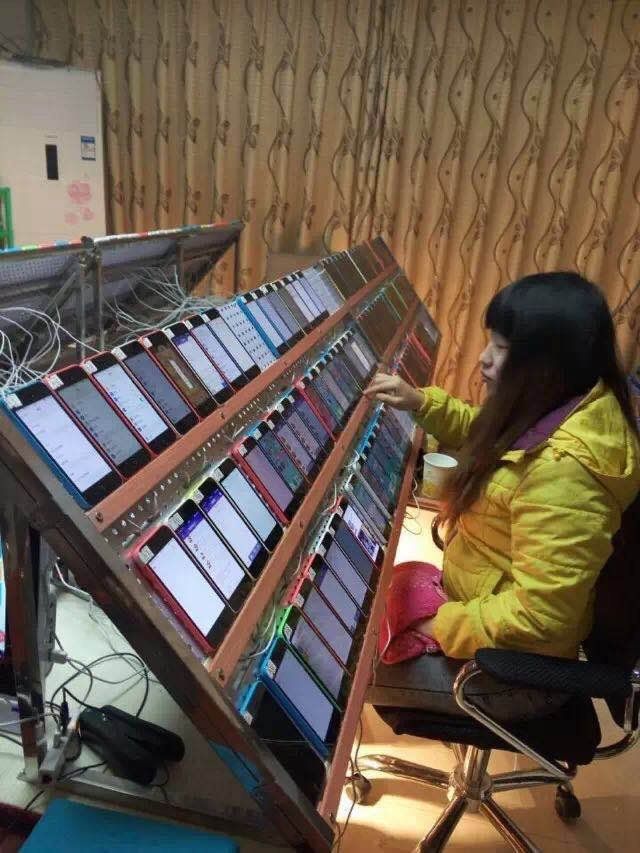
And for the testers requirement? Should every hobbyist developer be required to buy a dozen phones and set up one of those click farms that fraudsters use? Or are we fine with ending the era of hobbyist development?
CEO's exist as a sink for liability. When something goes wrong, they are the fall guys, that's ultimately their job. That's why CEO compensation is generally correlated strongly to earnings and they usually have golden parachutes.
Without a CEO to fire when the business goes south, how is the board supposed to respond? Taking accountability? lmao
If you want something that displaces adenosine from your neurons you are in luck, because it already exists and is very easy to get; It's called methamphetamine
There is already a mathematically secure algorithm for securing a message: One Time Pad. The problem is that OTP requires that the length of the key and the length of message must be the same, which is inconvenient for large amounts of data.
So the solution is to find algos that let you use a smaller key, but the side effect is that by pigeonhole principle, your keyspace is smaller than the message space, so it MUST be insecure. The trick is to make it so that it's only insecure enough that it's infeasible to break.
It's inconvenient for any amount of data, because it essentially begs the question; if you can securely transmit N bytes of key pad to a counterparty, just use that mechanism to transmit N bytes of plaintext instead.
It has the advantage that the key can be sent before the message is known. Think military battlefield. Your commander goes out to war with a CD, and then he can transmit messages like "we encountered the enemy". It would do no good to transmit "we encountered the enemy" before the war started.
an LLM would likely just converge on something like a shared prime GCD attack; basically finding private keys somewhere in their training set and then hoping that whatever keygen algo was setup incorrectly and used a shared seed.