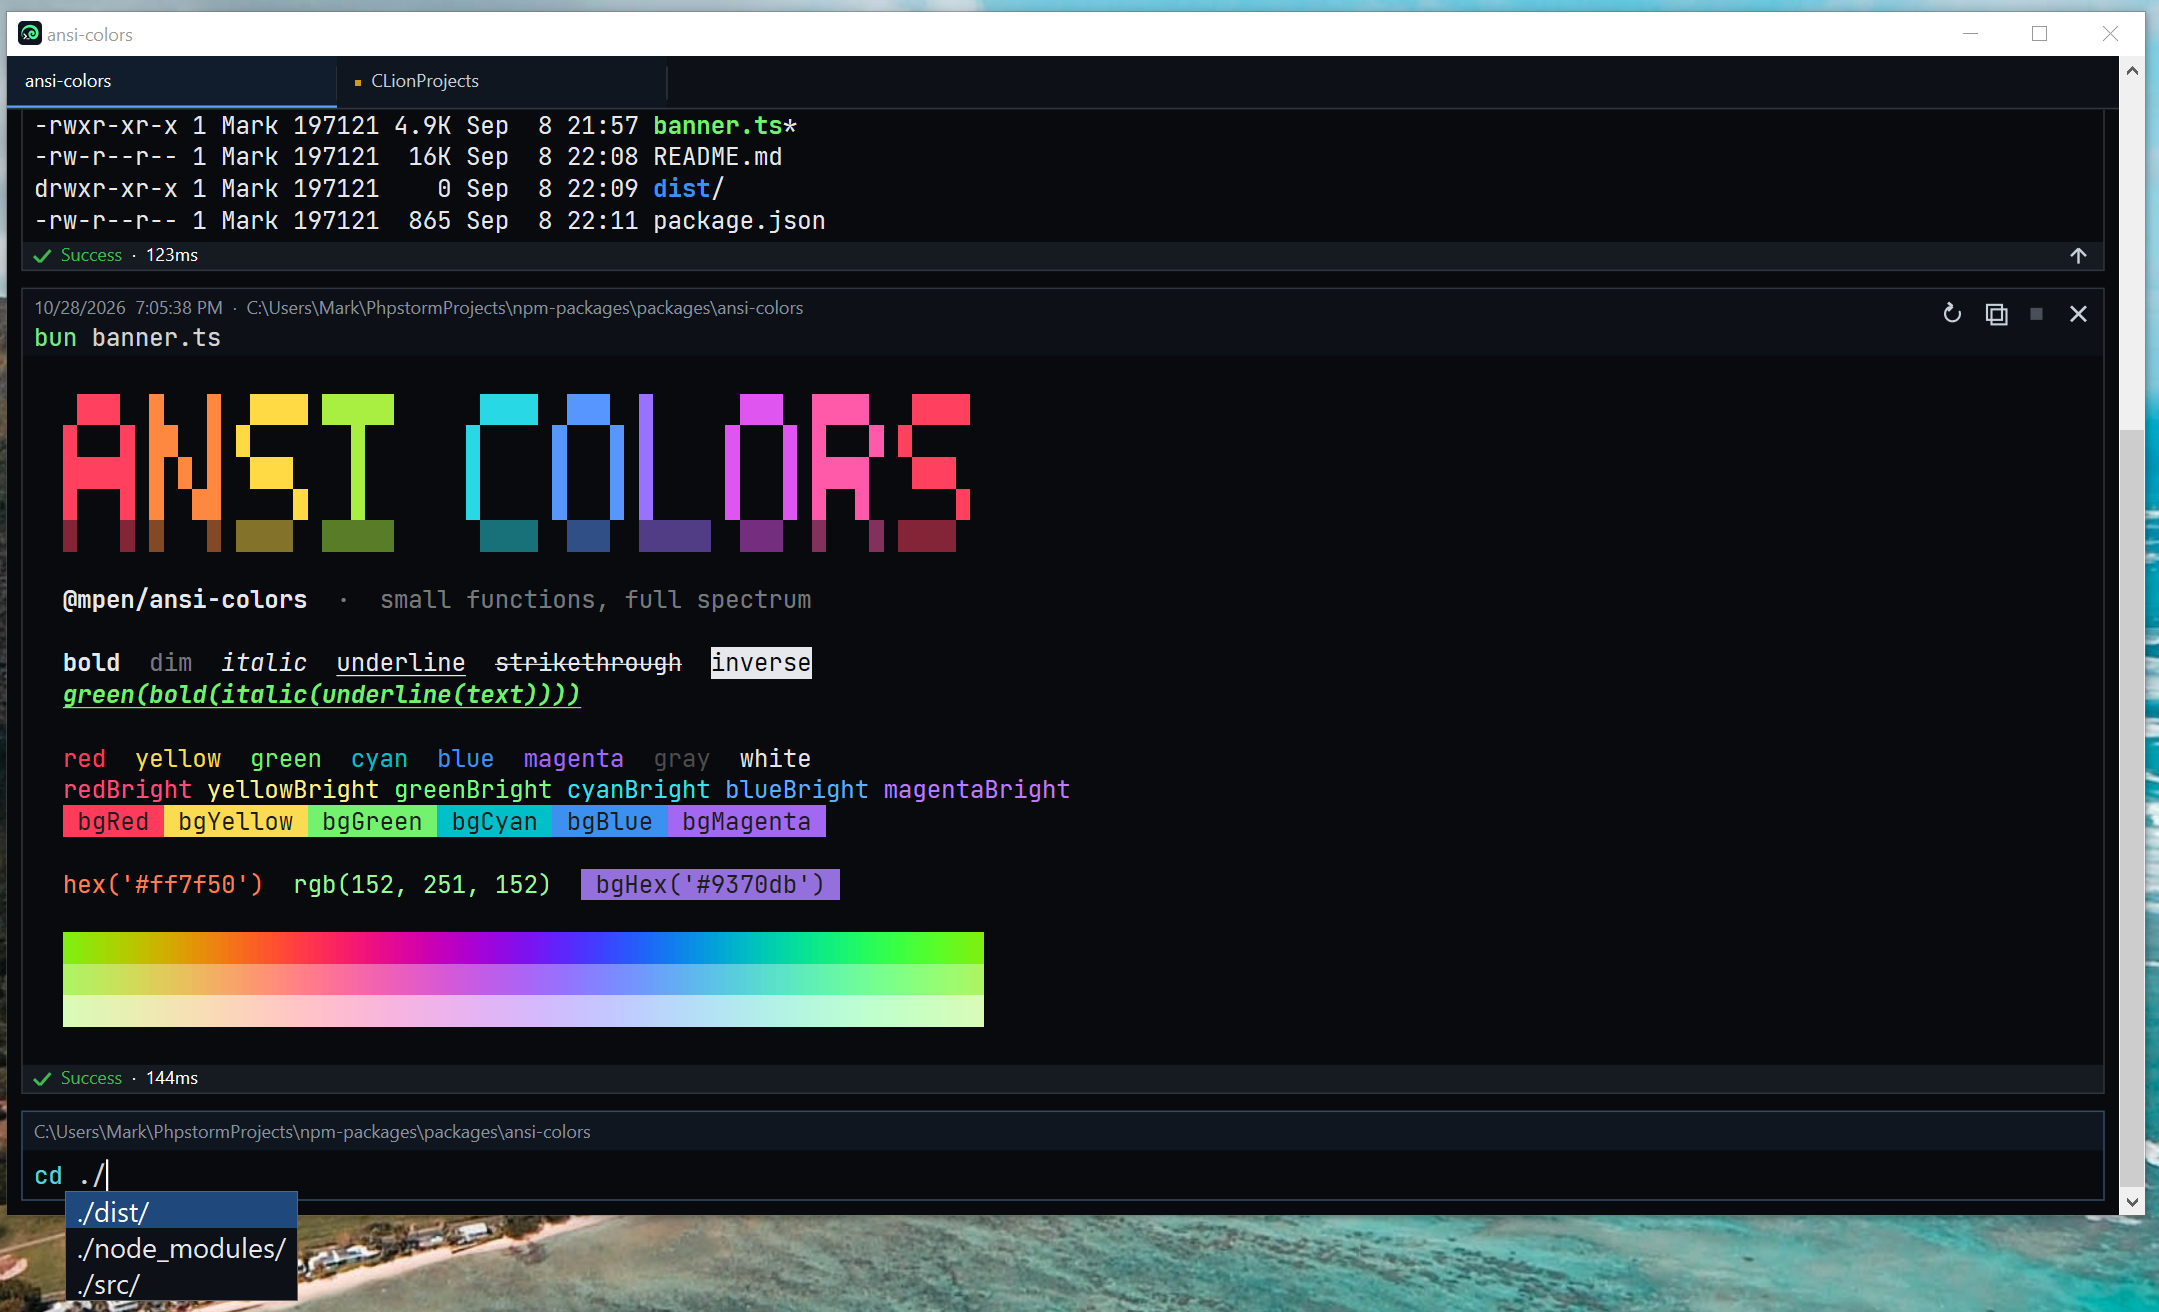
I haven't published it. It's a bit different than other terminals. Each program runs in its own box so you can run many commands concurrently without futzing about with additional tabs, or backgrounding, or tmux. It's got a Copy button on each which I absolutely love (useful for sending outputs to LLMs), a Restart button which is fantastic for restarting servers, scripts, and test runners. An 'X' for killing apps that don't want to die from Ctrl+C (or for exiting vim!). Native tab completions. Syntax & error highlighting as you type.
If that sounds interesting I might be willing to publish it, but I'll warn you now that it is vibe-coded. I've been iterating on it for a couple months now though and I think we've worked out pretty much all the kinks.
Would this technique work with inference optimization techniques like DFlash and MTP? In other words does it slow down things to the point where its just better to retry?
Yes, constrained decoding and speculative decoding work together, although they need to be carefully integrated and incorrect integrations give result in bugs (see point 3 under Section "Differences in Constrained-Decoding Behavior" in the blog post). Performance overhead does not generally seem to be a large problem. Of the speculative tokens, those that are not allowed by the grammar get discarded.
Both are actually already supported! We have pdf_decrypt (which unlocks password-protected PDFs given the password) and pdf_sign for applying cryptographic signatures, as well as pdf_validate_signatures for verifying certificates.


reply